
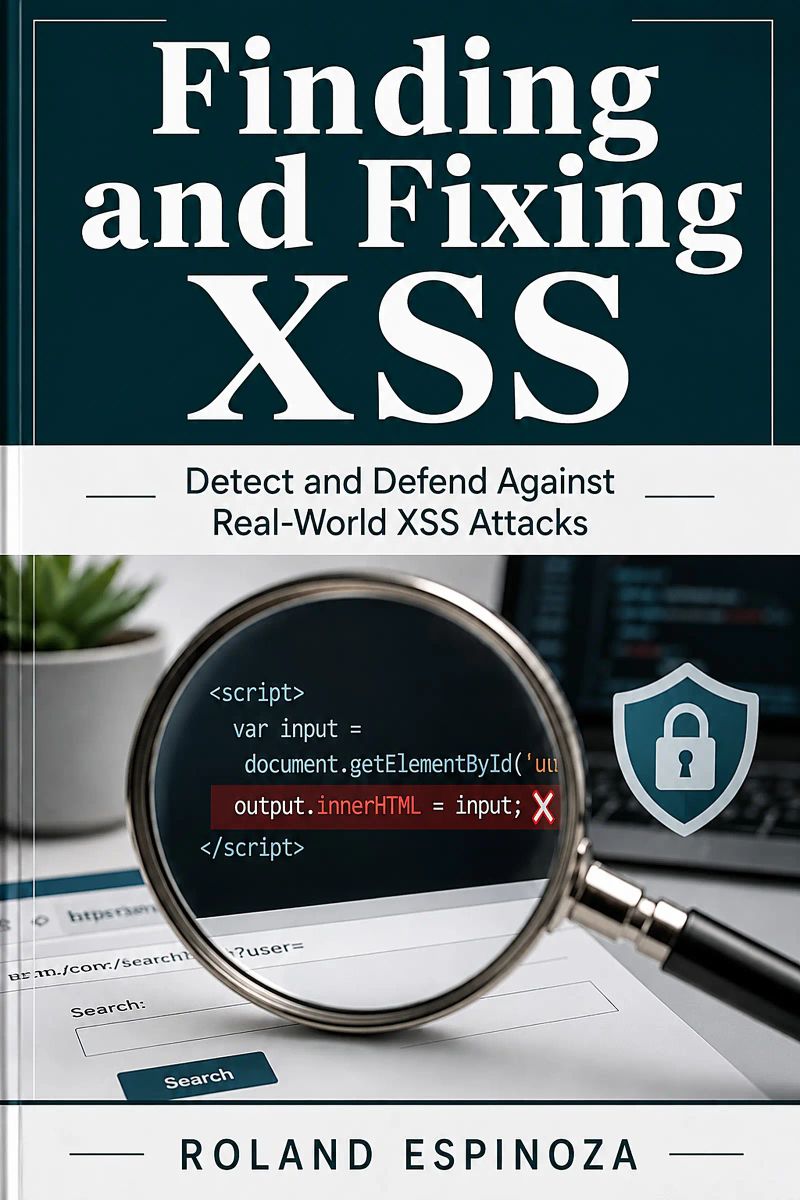
Finding and Fixing XSS
Detect and Defend Against Real-World XSS AttacksBy Roland Espinoza


Length8h 3m
About this audiobook
Cross-site scripting is the most pervasive web security flaw, and Finding and Fixing XSS is your hands-on guide to mastering its detection and remediation. Whether you are a beginner developer or a seasoned pro, this book teaches you how to find reflected and stored XSS in real-world applications—and, crucially, how to write fixes that actually close the vulnerability for good.
You will learn to spot XSS in every context: URL parameters, form inputs, JSON responses, and even inside JavaScript strings. Through practical examples and step-by-step walkthroughs, you will understand why common mitigations like HTML encoding or input validation often fail, and how to implement proper output encoding, content security policies, and secure-by-design patterns. Each chapter builds on the last, moving from simple reflected flaws to complex stored attacks that persist across sessions.
The book covers advanced topics such as DOM-based XSS, mutation XSS, and bypassing WAFs, all while emphasizing the mindset of a security engineer who thinks like an attacker. You will also get a complete toolkit for testing your own applications: browser extensions, fuzzing techniques, and automated scanners—but with the caveat that no tool replaces understanding.
Real-world case studies show how XSS was exploited in major breaches, and how the fixes were eventually applied. By the end, you will be able to audit any web application for XSS, write secure code from the start, and explain the risks to non-technical stakeholders. This is not just a theory book—it is a workbook you will keep open on your desk.
Competing titles like [placeholder] and [placeholder] cover XSS superficially, but this book goes deep into the mechanics of the attack and the exact code changes that close it. If you want to stop XSS for good, start here.
Audiobook details
GenreTechnology
Length8 hrs 3 mins
Narrated byListen with 1,000+ voices
FormateBook with Audio
LanguageEnglish
Table of contents
1Preface
2Chapter 1 — The Web Security Landscape – Why XSS Still Matters
3Chapter 2 — Setting Up Your Ethical Hacking Lab
4Chapter 3 — Core Concepts – How XSS Works
5Chapter 4 — Your First Payload – Reflected XSS in Action
Show all chaptersShow less
6Chapter 5 — Stored XSS – The Persistent Threat
7Chapter 6 — DOM-Based XSS – Client-Side Dangers
8Chapter 7 — Context Matters – Crafting Payloads for Different Sinks
9Chapter 8 — Escalation – From alert() to Data Theft
10Chapter 9 — Bypassing Filters and WAFs
11Chapter 10 — Advanced Exploitation – Session Hijacking and Worming
12Chapter 11 — Defense Foundations – Input Validation and Output Encoding
13Chapter 12 — Content Security Policy – Your Strongest Shield
14Chapter 13 — Secure Development Practices – Server-Side and Client-Side
15Chapter 14 — Automated Scanning and Manual Testing Techniques
16Chapter 15 — Real-World Case Studies and Bug Bounty Insights
17Chapter 16 — Securing WebForum – Applying All Defenses
18Chapter 17 — Continuous Security – Monitoring and Updating
19Chapter 18 — Future Trends and Your Security Career
20About the Author
Everybody Has a Podcast (Except You)Justin McElroy, Travis McElroy, Griffin McElroy5h 9m4.3 (2.3K)$24 · $0.00
Hands of TimeRebecca Struthers8h 8m4.4 (1.3K)$26 · $0.00
Never Lost AgainBill Kilday10h 1m4.4 (805)$29 · $0.00
How the Internet HappenedBrian McCullough13h 28m4.3 (2.7K)$23 · $0.00
Collected Writings of Nikola TeslaNikola Tesla, Thomas Commerford Martin21h 50m4.3 (1.7K)$1 · $0.00
Just AspireAjai Chowdhry9h 13m4.4 (260)$29 · $0.00
The Little Book of AliensAdam Frank8h 20m4.3 (1.3K)$26 · $0.00
The inventions, researches and writings of Nikola Tesla (Annotated)Thomas Commerford Martin16h 59m4.3 (1.3K)$2 · $0.00
KargilV.P. Malik15h 18m4.3 (2K)$24 · $0.00
Experiments with Alternating CurrentsNikola Tesla9h 16m4.3 (874)$1.99 · $0.00
Fire on the HorizonTom Shroder, John Konrad8h 23m4.3 (858)$26 · $0.00
The Smell of Kerosene (Annotated)National Aeronautics and Space Administration, Donald L. Mallick, Peter W. Merlin11h 32m4.3 (523)$2 · $0.00
The Boy Who Harnessed the WindWilliam Kamkwamba, Bryan Mealer10h 5m4.2 (78.9K)$29 · $0.00
Across the Airless WildsEarl Swift10h 8m4.3 (1.3K)$29 · $0.00
Console WarsBlake J. Harris20h 41m4.2 (13.7K)$46 · $0.00
Improvised Munitions HandbookU.S. Department of Defense4h 49m4.3 (1.6K)$1.99 · $0.00
Escaping GravityLori Garver10h 54m4.2 (2.2K)$20 · $0.00
Wireless WarsJonathan Pelson8h 2m4.3 (418)$20 · $0.00
Let There Be WaterSeth M. Siegel8h 36m4.2 (2.3K)$20 · $0.00
The PerfectionistsSimon Winchester11h 46m4.2 (9.9K)$29 · $0.00
You may also like
Pete the Cat's Not So Groovy DayJames Dean, Kimberly Dean7m4.3 (282)$4 · $0.00
Writer to WriterGail Carson Levine5h 40m4.2 (1.1K)$24 · $0.00
The 4 Percent UniverseRichard Panek10h 7m4.0 (9.5K)$20
The Case of the Murdered MuckrakerCarola Dunn8h 3m3.7 (3.9K)$20
Mystery in the ChannelFreeman Wills Crofts8h 49m3.8 (1.8K)$2 · $0.00

Pete the Cat and the Missing CupcakesJames Dean, Kimberly Dean5m4.5 (16K)$4 · $0.00
Have His CarcaseDorothy L. Sayers15h 40m4.2 (21.9K)$2 · $0.00
The Middle Temple MurderJ. S. Fletcher8h 25m3.9 (1.1K)$2 · $0.00
The Devil’s AdvocatesMichael S. Lief, H. Mitchell Caldwell21h 18m4.1 (313)$32
How to Make Money Flipping Designer Handbags - A Guide to Authentication, Condition Grading, Safe Cleaning, Pricing, and Confident ResaleJACK FLIPWELL9h 26m$7.90 · $0.00
How to Make Money Flipping Golf Equipment - How to Identify In-Demand Clubs, Avoid Counterfeits, Improve Condition, and Resell for ProfitJACK FLIPWELL8h 39m$7.90 · $0.00

Hill Street BluesBill Brown Jr.40m$4
Series 22 Exam Study GuideMarie Peterson9h 31m$10
How to Make Money Flipping Musical Instruments - How to Spot Desirable Models, Assess Condition, Add Value, and Sell to MusiciansJACK FLIPWELL8h 54m$7.90 · $0.00
A collection of Latin maxims & rules, in law and equityPeter Halkerston5h 3m$1 · $0.00

Introductory Address on the General Medical Council, its Powers and its WorkDonald MacAlister1h 6m$2 · $0.00

The mystery of the lost emeraldJonatas Eliakim4m$13
Legal ChemistryAlfred Naquet5h 53m$2 · $0.00
How to Make Money Flipping Jewelry - How to Test Metals and Stones, Spot Fakes, Value Pieces, and Sell SafelyJACK FLIPWELL8h 7m$7.90 · $0.00

Vanity Fair: November 2014 IssueVanity Fair5h 28m$7