
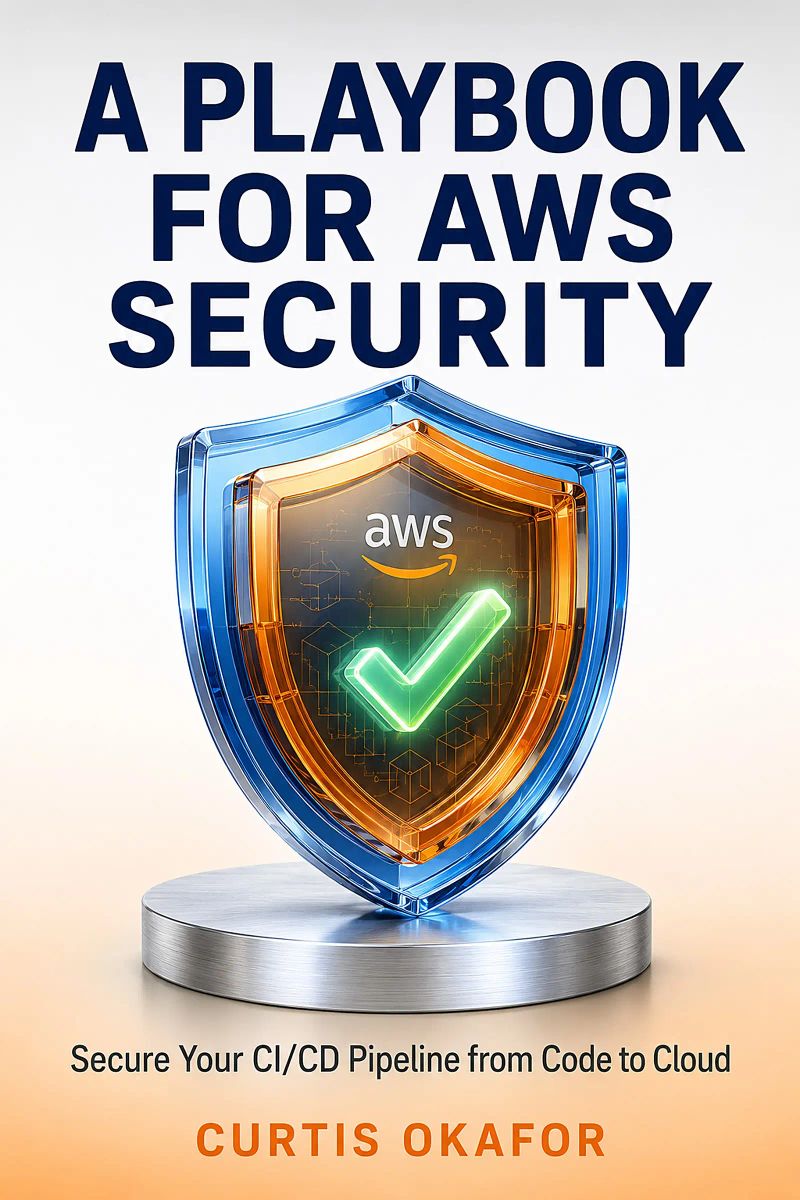
A Playbook for AWS Security
Secure Your CI/CD Pipeline from Code to CloudBy Curtis Okafor

Length8h 27m
About this audiobook
AWS security book and cloud security guide. Secure your AWS environment with A Playbook for AWS Security, a practical, hands-on guide that covers identity, network controls, encryption, logging, and the proactive defenses every AWS account needs. Whether you're a beginner or a seasoned DevOps professional, this book delivers actionable strategies to protect your cloud workloads, reduce risk, and achieve compliance. From setting up IAM policies to implementing VPC security groups, encrypting data at rest and in transit, and configuring CloudTrail and CloudWatch for continuous monitoring, you'll learn how to build a robust security posture. Unlike other titles that focus on theory, this playbook provides step-by-step instructions, real-world examples, and ready-to-use scripts that you can deploy immediately. Discover how to automate security checks with AWS Config, guard against common threats like DDoS and misconfigurations, and design incident response plans. With A Playbook for AWS Security, you'll move from reactive fixes to proactive protection, ensuring your infrastructure stays resilient. This book is your essential companion for mastering AWS security, whether you're managing a single account or a multi-account organization. Start securing your cloud today—no fluff, just practical defenses that work. Unlike Securing DevOps: Security in the Cloud and Cloud Native DevOps with Kubernetes, this book focuses exclusively on AWS-native tools and best practices, giving you a targeted approach to safeguarding your workloads.
Audiobook details
GenreTechnology
Length8 hrs 27 mins
Narrated byListen with 1,000+ voices
FormateBook with Audio
LanguageEnglish
Table of contents
1Introduction
2Preface
3Chapter 1 — Secure Foundations for DevOps
4Chapter 2 — Identity and Access Management for Pipelines
5Chapter 3 — Network Isolation with Amazon VPC
Show all chaptersShow less
6Chapter 4 — Infrastructure as Code with Guardrails
7Chapter 5 — Building a Secure CI/CD Pipeline
8Chapter 6 — Container Security from Build to Runtime
9Chapter 7 — Encrypting Everything in Transit and at Rest
10Chapter 8 — Monitoring and Logging for Pipeline Health and Security
11Chapter 9 — Threat Detection with Amazon GuardDuty and Security Hub
12Chapter 10 — Automated Incident Response Playbooks
13Chapter 11 — Compliance as Code with AWS Config
14Chapter 12 — Securing Serverless Components in the Pipeline
15Chapter 13 — Identity Federation and Single Sign-On Integration
16Chapter 14 — Disaster Recovery and Backup for Pipeline State
17Chapter 15 — Secrets Management close look
18Chapter 16 — Cost-Aware Security and Tagging Strategies
19Chapter 17 — Advanced Encryption: KMS, CloudHSM, and Envelope Encryption
20Chapter 18 — Continuous Security Audit and Improvement
21About the Author
Everybody Has a Podcast (Except You)Justin McElroy, Travis McElroy, Griffin McElroy5h 9m4.3 (2.3K)$24 · $0.00
Hands of TimeRebecca Struthers8h 8m4.4 (1.3K)$26 · $0.00
Never Lost AgainBill Kilday10h 1m4.4 (805)$29 · $0.00
How the Internet HappenedBrian McCullough13h 28m4.3 (2.7K)$23 · $0.00
Collected Writings of Nikola TeslaNikola Tesla, Thomas Commerford Martin21h 50m4.3 (1.7K)$1 · $0.00
Just AspireAjai Chowdhry9h 13m4.4 (260)$29 · $0.00
The Little Book of AliensAdam Frank8h 20m4.3 (1.3K)$26 · $0.00
The inventions, researches and writings of Nikola Tesla (Annotated)Thomas Commerford Martin16h 59m4.3 (1.3K)$2 · $0.00
KargilV.P. Malik15h 18m4.3 (2K)$24 · $0.00
Experiments with Alternating CurrentsNikola Tesla9h 16m4.3 (874)$1.99 · $0.00
Fire on the HorizonTom Shroder, John Konrad8h 23m4.3 (858)$26 · $0.00
The Smell of Kerosene (Annotated)National Aeronautics and Space Administration, Donald L. Mallick, Peter W. Merlin11h 32m4.3 (523)$2 · $0.00
The Boy Who Harnessed the WindWilliam Kamkwamba, Bryan Mealer10h 5m4.2 (78.9K)$29 · $0.00
Across the Airless WildsEarl Swift10h 8m4.3 (1.3K)$29 · $0.00
Console WarsBlake J. Harris20h 41m4.2 (13.7K)$46 · $0.00
Improvised Munitions HandbookU.S. Department of Defense4h 49m4.3 (1.6K)$1.99 · $0.00
Escaping GravityLori Garver10h 54m4.2 (2.2K)$20 · $0.00
Wireless WarsJonathan Pelson8h 2m4.3 (418)$20 · $0.00
Let There Be WaterSeth M. Siegel8h 36m4.2 (2.3K)$20 · $0.00
The PerfectionistsSimon Winchester11h 46m4.2 (9.9K)$29 · $0.00
You may also like
ITIL® 4 Create, Deliver and Support (CDS)Claire Agutter3h 36m4.6 (23)$40 · $0.00
Software Structure by DesignRohan Dasgupta14h 44m4.8 (10)$75
ITIL® 4 Essentials: Your essential guide for the ITIL 4 Foundation exam and beyond, second editionClaire Agutter4h4.2 (50)$40 · $0.00
HorizonsJames Poskett15h 18m3.7 (472)$33 · $0.00
A Color Notation: How to Numerically Describe ColorsA. H. Munsell3h 52m3.8 (159)$1.99 · $0.00
ChatGPT for Excel and Google SheetsImad Muratspahic6h 53m$11 · $0.00
Numerical Analysis Using MATLAB, Excel and VBAOmar Halabi12h 9m$75
Airfoils, Lift and Drag IllustratedPatrick Zwolinska11h 22m$50
Statistical Methods for Engineers and ScientistsPriya Ramanathan15h 5m$95
Blender for BeginnersImad Muratspahic1h 18m$5.20 · $0.00
AP Computer Science Principles Exam Study GuideMarie Peterson8h 32m$10
Invisible IncomeSara Melo1h 34m$1.80 · $0.00
From Zero To AutomaticSara Melo1h 25m$1.80 · $0.00
Operation ResearchKnowledge Flow1h 15m$4.10 · $0.00
Self Publishing: Optimize Your Entire Publishing Business With AI Assistants (How to Rise to the Top in Book Sales Through Creative Disruption)Peter Felts1h 8m$3.50 · $0.00
Algorithms in Java, Coded and TestedBianca Zielinski7h 25m$5 · $0.00
Machine Learning in the CloudLionel Jansen8h 21m$5 · $0.00
Build a 2.5D RPG with Godot 4 and C#Gregory Whitlock7h 8m$5 · $0.00
Bio-Inspired AI in C++Zoe Becker7h 10m$5 · $0.00
Python Programming Made PracticalAustin Gray7h 21m5.0 (1)$6.50 · $0.00