
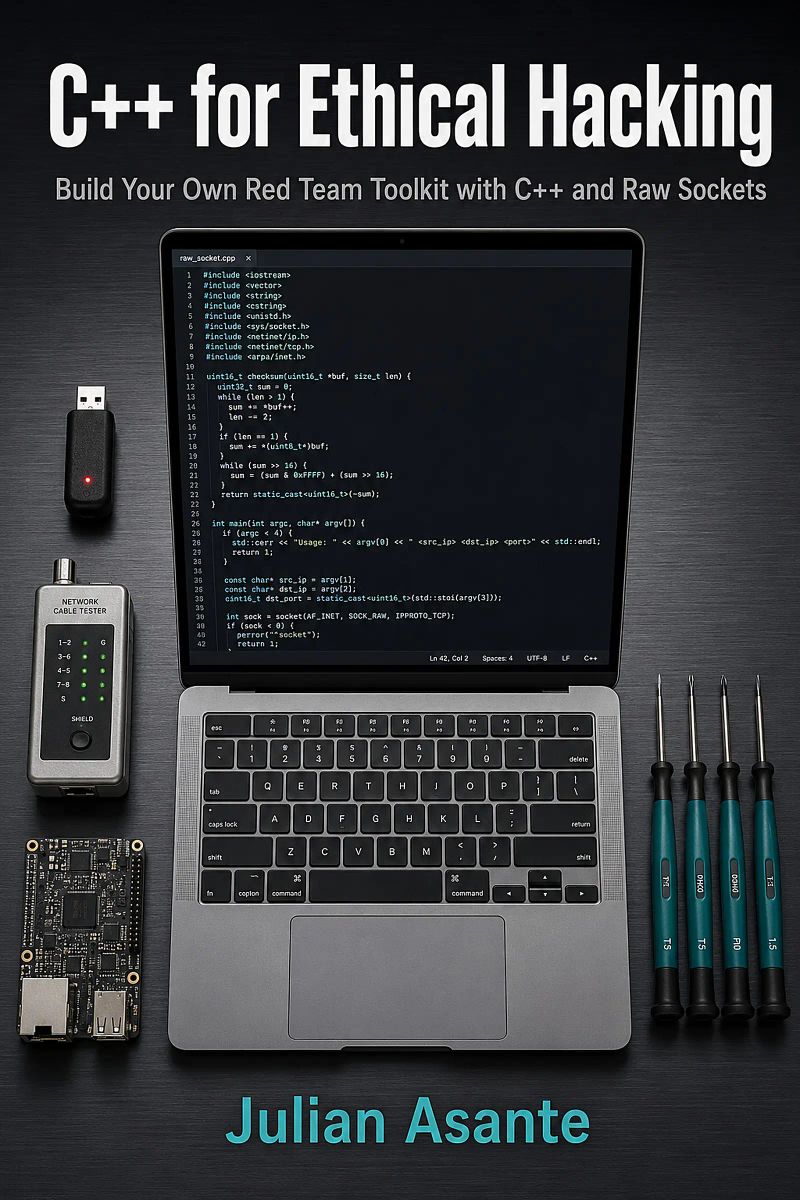
C++ for Ethical Hacking
Build Your Own Red Team Toolkit with C++ and Raw SocketsBy Julian Asante

Length7h 38m
About this audiobook
C++ for ethical hacking and penetration testing tools—learn offensive security by building real code. From port scanners to shellcode loaders, this hands-on guide takes you from beginner to pro in C/C++/.NET. Master network scanning, exploit development, and shellcode injection with practical projects. No fluff, just code that works. Start with a TCP scanner, then build a UDP sweeper, a multi-threaded port knocker, and a SYN flooder. Progress to process injection via DLLs, API hooking, and keyloggers. Finally, craft custom shellcode loaders and encryptors. Each chapter includes full source, explanations, and anti-detection tricks. Whether you're a security student or a professional red teamer, this book delivers real offensive skills. Competing with C# 14 and .NET 10 – Modern Cross-Platform Development Fundamentals and C# 12 and .NET 8 – Modern Cross-Platform Development Fundamentals, this is the only title focused on C++ for hacking.
This hands-on C/C++/C#/.NET guide is written to be used at the keyboard: every concept is paired with something you can run, adapt, and keep. You move from first principles to real, working results, with the common errors and fixes called out along the way so you are never stuck for long.
This hands-on C/C++/C#/.NET guide is written to be used at the keyboard: every concept is paired with something you can run, adapt, and keep. You move from first principles to real, working results, with the common errors and fixes called out along the way so you are never stuck for long.
Audiobook details
GenreTechnology
Length7 hrs 38 mins
Narrated byListen with 1,000+ voices
FormateBook with Audio
Publish dateSep 30, 2026
LanguageEnglish
Table of contents
1Preface
2Chapter 1 — Your Lab, Your Rules
3Chapter 2 — Raw Sockets: From Ping to Packet
4Chapter 3 — Scanner Core: Single-Threaded SYN Scanning
5Chapter 4 — Threads and Speed: Multi-Core Scanning
Mostrar todos os capítulosVer menos
6Chapter 5 — Event Loops for Thousands of Sockets
7Chapter 6 — Protocol Parsing: Service Fingerprinting
8Chapter 7 — Vulnerability Detection Engine
9Chapter 8 — Buffer Overflows: Exploitation from Scratch
10Chapter 9 — Process Manipulation: Hooks and Injection
11Chapter 10 — Custom Shells: Bind, Reverse, and Polymorphic
12Chapter 11 — Password Cracking: GPU-Accelerated Attacks
13Chapter 12 — Fuzzing: Finding Your Own Zero-Days
14Chapter 13 — Kernel Playground: Rootkits and Drivers
15Chapter 14 — Evading Defenders: Syscalls and Injection
16Chapter 15 — The Framework Shell: CLI and Lua Scripting
17Chapter 16 — Real-World Red Team Operations
18Chapter 17 — Polishing and Open-Sourcing
19Chapter 18 — The Road Ahead
20About the Author
LiftoffEric Berger9h 4m4.6 (9.5K)$29 · $0.00
The Honey BusMeredith May9h 31m4.4 (16.6K)$25 · $0.00
Collected Writings of Nikola TeslaThomas Commerford Martin, Nikola Tesla19h 42m4.4 (2.8K)$1.99 · $0.00
Operation PedestalMax Hastings12h 29m4.4 (5.2K)$29 · $0.00
When the Heavens Went on SaleAshlee Vance18h 20m4.4 (3K)$40 · $0.00
Everybody Has a Podcast (Except You)Justin McElroy, Travis McElroy, Griffin McElroy5h 9m4.3 (2.3K)$24 · $0.00
Hands of TimeRebecca Struthers8h 8m4.4 (1.3K)$26 · $0.00
Never Lost AgainBill Kilday10h 1m4.4 (805)$29 · $0.00
How the Internet HappenedBrian McCullough13h 28m4.3 (2.7K)$23 · $0.00
Collected Writings of Nikola TeslaNikola Tesla, Thomas Commerford Martin21h 50m4.3 (1.7K)$1 · $0.00
Just AspireAjai Chowdhry9h 13m4.4 (260)$29 · $0.00
The Little Book of AliensAdam Frank8h 20m4.3 (1.3K)$26 · $0.00
The inventions, researches and writings of Nikola Tesla (Annotated)Thomas Commerford Martin16h 59m4.3 (1.3K)$2 · $0.00
KargilV.P. Malik15h 18m4.3 (2K)$24 · $0.00
Experiments with Alternating CurrentsNikola Tesla9h 16m4.3 (874)$1.99 · $0.00
Fire on the HorizonTom Shroder, John Konrad8h 23m4.3 (858)$26 · $0.00
The Smell of Kerosene (Annotated)National Aeronautics and Space Administration, Donald L. Mallick, Peter W. Merlin11h 32m4.3 (523)$2 · $0.00
The Boy Who Harnessed the WindWilliam Kamkwamba, Bryan Mealer10h 5m4.2 (78.9K)$29 · $0.00
Across the Airless WildsEarl Swift10h 8m4.3 (1.3K)$29 · $0.00
Console WarsBlake J. Harris20h 41m4.2 (13.7K)$46 · $0.00
You may also like
Collected Writings of Nikola TeslaThomas Commerford Martin, Nikola Tesla19h 42m4.4 (2.8K)$1.99 · $0.00
Day Trading AttentionGary Vaynerchuk8h 25m4.3 (1.8K)$28 · $0.00
Optical Transceivers and Photonic CircuitsAmara Okonkwo13h 9m$75
Modern Data EngineeringOwen Fletcher7h 33m$6.50 · $0.00
Practical SQL; Query & Manage DatabaseStephen Hart5h 56m$7 · $0.00
Blockchain : The technology that will transform commerceUnknown Author1h 9m$17 · $0.00
The Evolution of Technologythe Speech Resource Company9h 30m$20
Building and Welding ShipsHalvard Brekkeng16h 54m$90
Linux For BeginnersRodrigo Montini3h 9m$7 · $0.00
A-B-C of ElectricityWm. H. Meadowcroft2h 35m3.9 (159)$1 · $0.00
Modeling Human-Structure Interaction Using a Controller SystemAlbert Ricardo Ortíz Lasprilla1h 56m$12 · $0.00

The peaceful atomBernice Kohn Hunt54m$2 · $0.00
Async JavaScript, UntangledVictor Fontaine7h 36m$5 · $0.00
The Boy's Book of Industrial InformationElisha Noyce7h 48m$2 · $0.00
Study of a reluctance magnetic gearbox for energy storage system applicationBruno Fensterseifer Dias2h 14m$20 · $0.00
On the Construction of Catalogues of LibrariesCharles C. Jewett4h$2 · $0.00
Thomas Alva Edison: A short biography5 Minutes, 5 Minute Biographies, George Fritsche5m$1 · $0.00
Eu Gmp Annex 13 (Investigational Medicinal Products , Complexity Meets Reality)Unknown Author1h 35m$19 · $0.00
DCF BudgetingIsabella S. Lee8h 1m$6.30 · $0.00
Optimal Design and Control MathHenrik Solberg14h 48m$90