
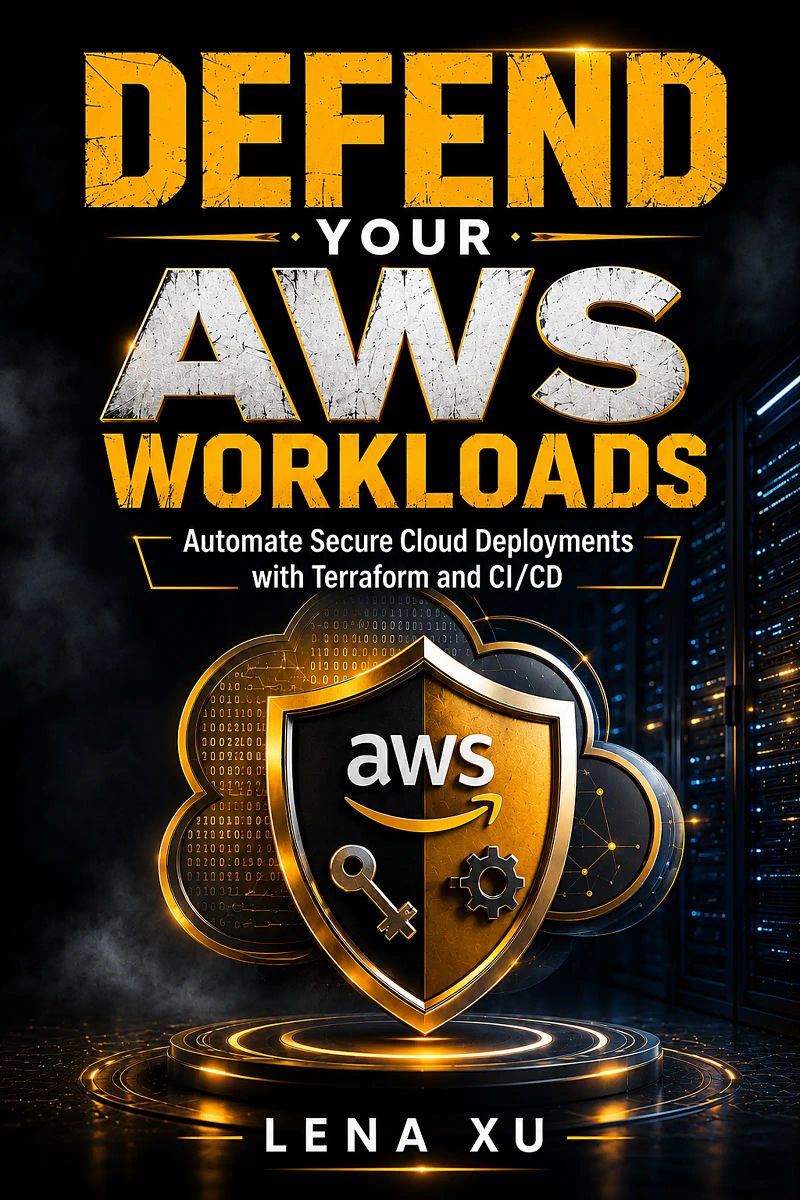
Defend Your AWS Workloads
Automate Secure Cloud Deployments with Terraform and CI/CDBy Lena Xu


Length8h 12m
About this audiobook
AWS security and cloud threat detection are critical for every DevOps team. In Defend Your AWS Workloads, Lena Xu delivers a hands-on guide to protecting, detecting, and responding to live threats on AWS. From IAM hardening and encryption to GuardDuty and real-world security operations, this book takes you from beginner to pro. You'll learn how to automate incident response, secure CI/CD pipelines, and audit your environment against production demands. Unlike Gene Kim (The DevOps Handbook) and Julien Vehent (Securing DevOps), this book focuses exclusively on AWS-native tools and live threat scenarios. Whether you're a developer, SRE, or security engineer, you'll get actionable strategies to defend your workloads today.
What You'll Learn
Implement IAM policies and encryption for AWS services
Set up GuardDuty, CloudTrail, and Security Hub for detection
Respond to incidents with automated playbooks
Secure Kubernetes and serverless workloads on AWS
Comply with SOC 2, PCI DSS, and GDPR in the cloud
Who This Book Is For
DevOps engineers, cloud architects, and security professionals who want to master AWS security operations. No prior security experience required—just basic AWS knowledge.
Stop guessing and start defending. Lena Xu shows you how to outsmart attackers with proven techniques. Get your copy of Defend Your AWS Workloads today.
This hands-on Cloud/DevOps guide is written to be used at the keyboard: every concept is paired with something you can run, adapt, and keep. You move from first principles to real, working results, with the common errors and fixes called out along the way so you are never stuck for long.
Audiobook details
GenreTechnology
Length8 hrs 12 mins
Narrated byListen with 1,000+ voices
FormateBook with Audio
LanguageEnglish
Table of contents
1Introduction
2Preface
3Chapter 1 — Cloud DevOps Landscape: Why Security Must Be Embedded
4Chapter 2 — Setting Up Your Secure DevOps Environment
5Chapter 3 — Infrastructure as Code (IaC) with Security: Terraform for VPC, IAM, and Encryption
Show all chaptersShow less
6Chapter 4 — Identity and Access Management for DevOps
7Chapter 5 — Secure Networking: VPC Design with Private Subnets, NACLs, and Security Groups
8Chapter 6 — Continuous Integration: Secure Code Repositories and Build Pipelines
9Chapter 7 — Container Security: Docker, Amazon ECR, and Image Scanning
10Chapter 8 — Orchestration Security: Amazon EKS with Pod Security Policies
11Chapter 9 — Continuous Deployment: Blue/Green Deployments and Safe Rollbacks
12Chapter 10 — Secrets Management: AWS Secrets Manager and Parameter Store
13Chapter 11 — Monitoring and Logging: CloudWatch, CloudTrail, and Centralized Logging
14Chapter 12 — Threat Detection: GuardDuty, Security Hub, and Automated Response
15Chapter 13 — Compliance as Code: AWS Config Rules and Custom Policies
16Chapter 14 — Backup and Disaster Recovery: Automating Backups and Cross-Region Replication
17Chapter 15 — Security Testing in the Pipeline: SAST, DAST, and Vulnerability Scanning
18Chapter 16 — Incident Response Runbooks: Automating Remediation with Lambda
19Chapter 17 — Cost Management and Security: Balancing Trade-offs
20Chapter 18 — Next Steps: Continuous Improvement and Certification Paths
21About the Author
Hands of TimeRebecca Struthers8h 8m4.4 (1.3K)$26 · $0.00
Never Lost AgainBill Kilday10h 1m4.4 (805)$29 · $0.00
How the Internet HappenedBrian McCullough13h 28m4.3 (2.7K)$23 · $0.00
Collected Writings of Nikola TeslaNikola Tesla, Thomas Commerford Martin21h 50m4.3 (1.7K)$1 · $0.00
Just AspireAjai Chowdhry9h 13m4.4 (260)$29 · $0.00
The Little Book of AliensAdam Frank8h 20m4.3 (1.3K)$26 · $0.00
The inventions, researches and writings of Nikola Tesla (Annotated)Thomas Commerford Martin16h 59m4.3 (1.3K)$2 · $0.00
KargilV.P. Malik15h 18m4.3 (2K)$24 · $0.00
Experiments with Alternating CurrentsNikola Tesla9h 6m4.3 (874)$1 · $0.00
Fire on the HorizonTom Shroder, John Konrad8h 23m4.3 (858)$26 · $0.00
The Smell of Kerosene (Annotated)National Aeronautics and Space Administration, Donald L. Mallick, Peter W. Merlin11h 32m4.3 (523)$2 · $0.00
The Boy Who Harnessed the WindWilliam Kamkwamba, Bryan Mealer10h 5m4.2 (78.9K)$29 · $0.00
Across the Airless WildsEarl Swift10h 8m4.3 (1.3K)$29 · $0.00
Console WarsBlake J. Harris20h 41m4.2 (13.7K)$46 · $0.00
Improvised Munitions HandbookU.S. Department of Defense4h 49m4.3 (1.6K)$1.99 · $0.00
Escaping GravityLori Garver10h 54m4.2 (2.2K)$20 · $0.00
Wireless WarsJonathan Pelson8h 2m4.3 (418)$20 · $0.00
Let There Be WaterSeth M. Siegel8h 36m4.2 (2.3K)$20 · $0.00
The PerfectionistsSimon Winchester11h 46m4.2 (9.9K)$29 · $0.00
Rethinking NarcissismDr. Craig Malkin6h 7m4.2 (3.4K)$24 · $0.00
You may also like
Experiments with Alternating CurrentsNikola Tesla9h 6m4.3 (874)$1 · $0.00
The Modern American Pistol and RevolverArthur Corbin Gould2h 37m$2 · $0.00

Torpedoes and Torpedo WarfareC. W. Sleeman14h 18m$2.30
Battle of AlgorithmsIsla L. Gallagher3h 43m$4.10 · $0.00
Build a Real-World App with ASP.NET CoreTheo Calderon8h 19m$5 · $0.00
Async Python for BeginnersAdrian Okafor7h 27m$5 · $0.00
Pass the CKAD ExamMarcus Iqbal8h 9m$5 · $0.00
JavaScript. A Comprehensive manual for creating dynamic, responsive websites and applicationsIbrahim Nugwa Abdulrazak8h 38m$17 · $0.00
Emerson Radio Model 39 Warranty CardAnonymous3m$2 · $0.00
Build. Test. Secure. Ship.""Alex Renner10h 5m$11.50 · $0.00
What Every Housewife Should Know About Electric Cooking (1945)General Motors Corporation. Frigidaire Division45m$1 · $0.00
Governance of Enterprise IT based on COBIT 5Geoff Harmer3h 9m3.2 (44)$34 · $0.00
The 2020 WorkplaceJeanne C. Meister, Karie Willyerd9h 44m3.8 (574)$29 · $0.00
Delco Radio Owner's Manual Model 633; Delcotron Generator InstallationDelco-Remy Corporation28m$2 · $0.00
Electric Transmission of Water PowerAlton D. Adams9h 50m$2 · $0.00
Electric Power Substations Step by StepObed Kimathi14h 17m$65
How to Learn About Blockchain and Cryptocurrencies in 48 Hours or LessUnknown Author44m$17 · $0.00
Modern MarvelsJulie Murray20m$3
The Art of IllustrationHenry Blackburn2h 51m4.2 (18)$2 · $0.00
Async JavaScript, UntangledVictor Fontaine7h 36m$5 · $0.00