
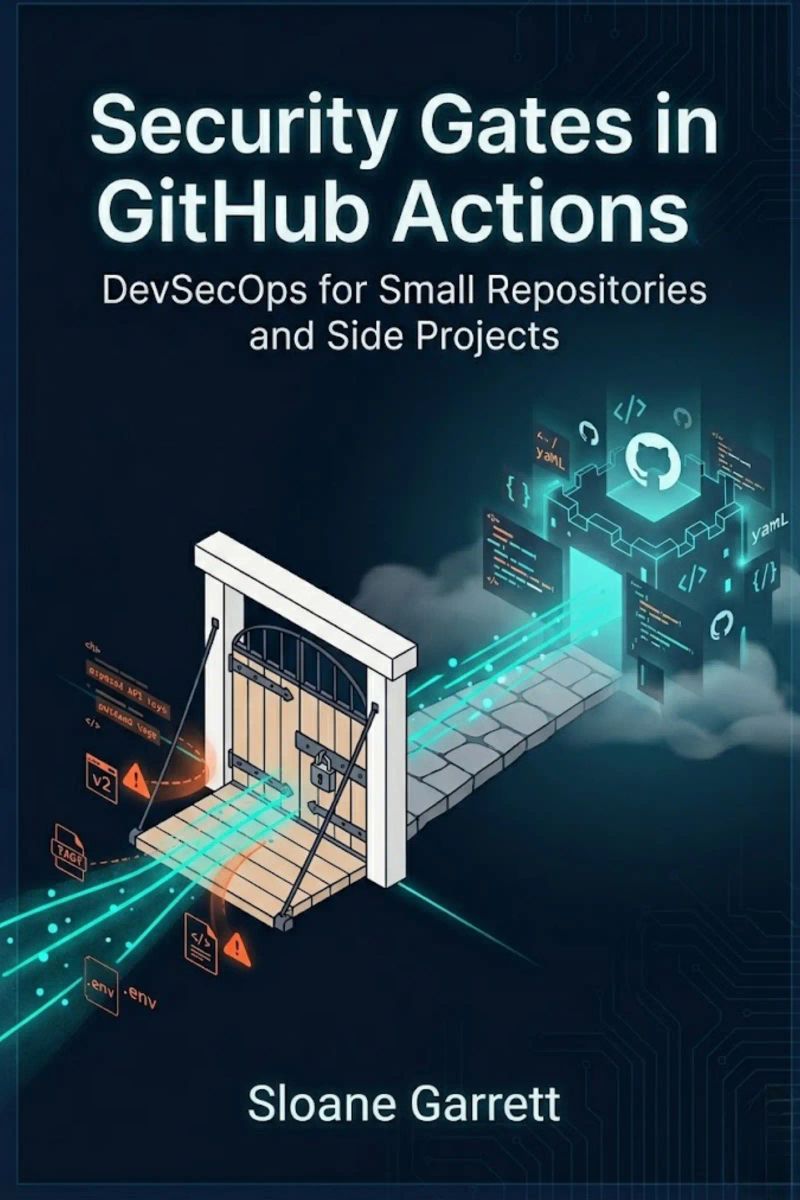
Security Gates in GitHub Actions
DevSecOps for Small Repositories and Side ProjectsBy Sloane Garrett


Length7h 54m
About this audiobook
What if the next npm install you run silently adds a backdoor to your side project — and you don't notice until your API keys are on the dark web?
Your GitHub repository has a secret problem. Not the kind you store in Settings > Secrets. The kind where your package-lock.json pins 47 vulnerable packages, your actions/checkout@v2 was deprecated six months ago, and that "helpful" contributor last week added a dependency with a post-install script that phones home.
You don't have a security team. You don't have a SOC 2 budget. What you have is this book — a field manual for solo developers who refuse to let their side projects become someone else's breach vector.
Inside, you'll build automated security gates that catch the mistakes you make at 11 PM: dependency audits that fail CI before vulnerable code merges, secret scanners that block API keys before they reach GitHub's servers, container image scanners that find CVEs in your Docker base layers, and incident response playbooks that fit on one page because you don't have time for forty.
Every chapter includes real, runnable YAML workflows and Python scripts — not theory. You'll harden pull requests, enforce third-party action policies, set up canary deployments with automatic rollback, and generate SBOMs that prove your supply chain transparency. You'll learn when to patch immediately, when to document and wait, and when a simple sha256sum beats enterprise attestation.
Stop pushing secrets at midnight — pre-commit hooks and CI scans that catch leaks before they fossilize in Git history
Turn your pull request into a security checkpoint — required status checks that block merges until vulnerabilities, secrets, and static analysis pass
Harden your .github/workflows folder — action pinning, SHA verification, and policies that prevent the next tj-actions supply chain attack
Deploy with a safety net — canary health checks, automatic rollback, and .env validation that stops production crashes
Build metrics that matter — weekly MTTP tracking, dependency freshness scores, and a 5-minute daily checklist that keeps your repo safer than most enterprise codebases
Your repository is already under attack — by automated scanners, by compromised dependencies, by your own 2 AM fatigue. Build the gates now. Before the alert that wakes you up.
Audiobook details
GenreTechnology
Length7 hrs 54 mins
Narrated byListen with 1,000+ voices
FormateBook with Audio
Publish dateJun 8, 2026
LanguageEnglish
Table of contents
1DevSecOps for Small Repositories and Side Projects
2Sloane Garrett: TABLE OF CONTENTS
3PART I: THE FOUNDATION
4Introduction: The $0 Security Budget
5Chapter 1: The 3 AM Dependency Alert
Mostrar todos os capítulosVer menos
6Chapter 3: Secrets Leak in Plain Sight
7Chapter 4: The Trust Problem with Third-Party Actions
8PART II: THE GATES
9Chapter 5: The Pull Request as a Security Checkpoint
10Chapter 6: Dependency Lockfiles Are a Lie
11Chapter 7: Container Images Nobody Audits
12Chapter 8: The Code Review That Isn't
13Chapter 10: The Incident Response Playbook for One Person
14PART III: THE REAL WORLD
15Chapter 11: The Monorepo Problem
16Chapter 12: The Open Source Trap
17Chapter 13: The Legacy Repo Resurrection
18Chapter 14: The Side Project That Became a Product
19Chapter 15: The Compliance You Didn't Ask For
20PART IV: THE ADVANCED GUARDRAILS
21Chapter 16: The Supply Chain You Didn't Know You Had
22Chapter 17: The Self-Hosted Runner Dilemma
23Chapter 18: The Security Metrics That Matter
24Conclusion: The Gatekeeper's Mindset
More from Sloane Garrett
Augmented Reality und Computer Vision Wie AR-Anwendungen die reale Welt verstehen, um virtuelle Objekte nahtlos zu integrierenSloane Garrett8h 50m$14 · $0.00
Automatisierte Textklassifizierung Wie man Dokumente, Tickets und Nachrichten mit überwachtem Lernen automatisch kategorisiertSloane Garrett7h 40m$10.20 · $0.00
Edge-AI-Engineering Wie man Künstliche Intelligenz am Netzwerkrand Aufbaut, Bereitstellt und OptimiertSloane Garrett6h 33m$13 · $0.00
Grundlagen der 3D-Computer Vision Tiefenschätzung, Punktwolkenverarbeitung und Volumetrische Rekonstruktion aus KameraanordnungenSloane Garrett7h 59m$13 · $0.00
Eingebettetes Machine Learning Vereinfacht Von Sensordaten zu Intelligenten Entscheidungen auf Ressourcenbeschränkter HardwareSloane Garrett8h 13m$12
Dialogsysteme und Chatbots Design konversationeller KI, die Kontext Versteht, Sich an Verlauf Erinnert und Natürlich AntwortetSloane Garrett8h 43m$15
When the Heavens Went on SaleAshlee Vance18h 20m4.4 (3K)$40 · $0.00
Everybody Has a Podcast (Except You)Justin McElroy, Travis McElroy, Griffin McElroy5h 9m4.3 (2.3K)$24 · $0.00
Hands of TimeRebecca Struthers8h 8m4.4 (1.3K)$26 · $0.00
Never Lost AgainBill Kilday10h 1m4.4 (805)$29 · $0.00
How the Internet HappenedBrian McCullough13h 28m4.3 (2.7K)$23 · $0.00
Collected Writings of Nikola TeslaNikola Tesla, Thomas Commerford Martin21h 50m4.3 (1.7K)$1 · $0.00
Just AspireAjai Chowdhry9h 13m4.4 (260)$29 · $0.00
The Little Book of AliensAdam Frank8h 20m4.3 (1.3K)$26 · $0.00
The inventions, researches and writings of Nikola Tesla (Annotated)Thomas Commerford Martin16h 59m4.3 (1.3K)$2 · $0.00
KargilV.P. Malik15h 18m4.3 (2K)$24 · $0.00
Experiments with Alternating CurrentsNikola Tesla9h 16m4.3 (874)$1.99 · $0.00
Fire on the HorizonTom Shroder, John Konrad8h 23m4.3 (858)$26 · $0.00
The Smell of Kerosene (Annotated)National Aeronautics and Space Administration, Donald L. Mallick, Peter W. Merlin11h 32m4.3 (523)$2 · $0.00
The Boy Who Harnessed the WindWilliam Kamkwamba, Bryan Mealer10h 5m4.2 (78.9K)$29 · $0.00
Across the Airless WildsEarl Swift10h 8m4.3 (1.3K)$29 · $0.00
Console WarsBlake J. Harris20h 41m4.2 (13.7K)$46 · $0.00
Improvised Munitions HandbookU.S. Department of Defense4h 49m4.3 (1.6K)$1.99 · $0.00
Escaping GravityLori Garver10h 54m4.2 (2.2K)$20 · $0.00
Wireless WarsJonathan Pelson8h 2m4.3 (418)$20 · $0.00
Let There Be WaterSeth M. Siegel8h 36m4.2 (2.3K)$20 · $0.00